
The NIST AI Risk Management Framework (AI RMF) is a voluntary framework published by the National Institute of Standards and Technology in January 2023 that gives organizations a structure for managing risk across an AI system's lifecycle. It is organized around four functions, Govern, Map, Measure, and Manage, and is used to build and evaluate trustworthy AI.
What Is the NIST AI Risk Management Framework?
NIST built the AI RMF for any organization that designs, develops, deploys, or uses AI systems, regardless of industry or company size. The framework does not certify products or grant compliance status. It gives teams a common vocabulary and a repeatable process for identifying AI risk, deciding how much of that risk is acceptable, and documenting the decision.
For regulated industries, that documentation matters as much as the risk reduction itself. When an examiner, auditor, or enterprise client asks how an AI system was evaluated before it touched customer data or investment decisions, NIST's own AI RMF documentation gives a structure to point to. NIST extended the framework in July 2024 with a Generative AI Profile that addresses risks specific to generative models, covered in more detail below.
The Four Core Functions of the NIST AI RMF
The NIST AI Risk Management Framework organizes its guidance into four functions that apply continuously across an AI system's lifecycle, not as a one time checklist.
| FUNCTION | WHAT IT COVERS | EXAMPLE ACTIVITY |
|---|---|---|
| GOVERN | Organizational policy, accountability, and risk culture for AI | Defining who approves a new AI use case before it goes live |
| MAP | Context, stakeholders, and potential harms for a specific AI system | Documenting what data a vendor's AI model touches and where it is processed |
| MEASURE | Qualitative and quantitative evaluation of identified risks | Testing a model's outputs for accuracy and bias before deployment |
| MANAGE | Prioritizing and mitigating risk, and feeding lessons back into governance | Building an incident response and rollback plan for AI failures |
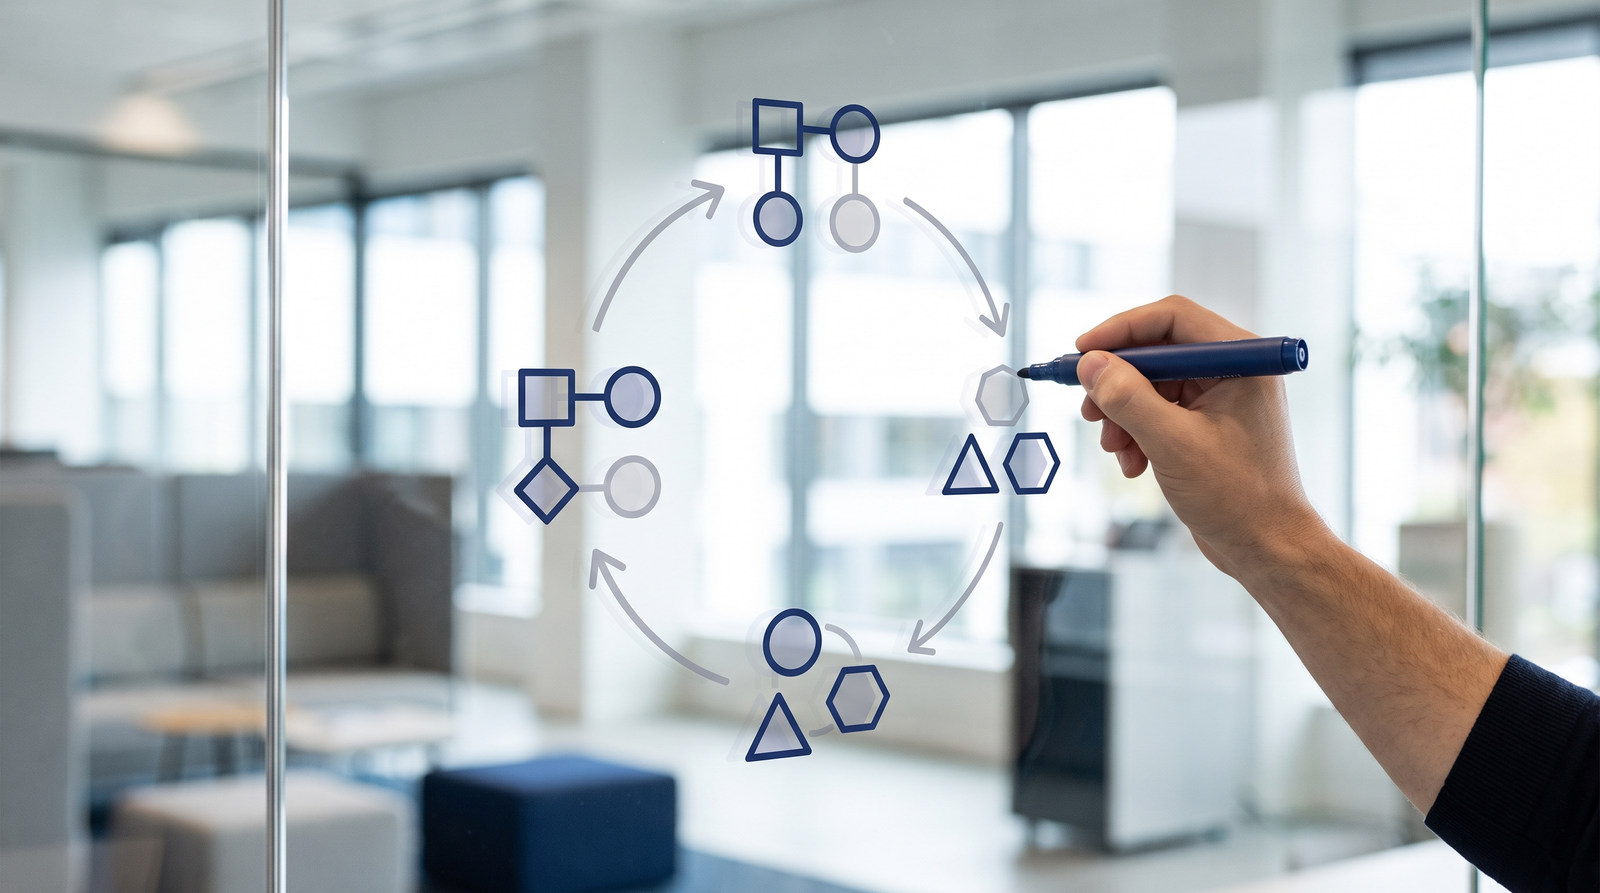
Govern
Govern is the foundation the other three functions sit on. It covers the policies, roles, and risk tolerance decisions an organization makes before a single AI system is evaluated, including who has authority to approve a high risk use case and how AI risk fits into the broader enterprise risk program.
Map
Map is where a team documents the specific context an AI system will operate in: what data it touches, who is affected by its output, and what could go wrong. This is the function most relevant to third party AI, since it is where an organization records what a vendor's model actually does with its data.
Measure
Measure applies testing and metrics to the risks identified in Map. That can include accuracy testing, bias testing, red teaming, and ongoing monitoring for drift once a model is in production.
Manage
Manage is where risk decisions turn into action: accepting, mitigating, transferring, or avoiding a given risk, and building the incident response and rollback plans that let a team react quickly when something goes wrong.
The Generative AI Profile (NIST AI 600-1)
Generative AI introduced risks the original 2023 framework did not fully address, including confabulation, which is fluent and confident output that is factually wrong, along with the disclosure of sensitive training data and questions about content provenance. NIST's Generative AI Profile, published in July 2024 as NIST AI 600-1, maps those risks onto the same four functions and gives organizations specific actions for each one. For proposal, DDQ, and security questionnaire teams, the profile is directly relevant: an AI tool that drafts a compliance answer with a confabulated detail can turn into a false representation in a signed document. This risk is closely related to shadow AI, the unapproved use of AI tools at work, covered in our guide to shadow AI in regulated industries.
Seven Characteristics of Trustworthy AI Under the NIST AI RMF
The AI RMF defines trustworthy AI through seven characteristics that the Measure and Manage functions are built to test for. A system should be valid and reliable, performing as intended and consistently over time. It should be safe, meaning it does not endanger human life, health, property, or the environment under defined conditions. It should be secure and resilient, protecting data confidentiality, integrity, and availability, and degrading safely under attack or failure. It should be accountable and transparent, with the organization able to explain how the system was designed, what data trained it, and who is responsible for its output. It should be explainable and interpretable, so its decisions can be understood in the context they are used. It should be privacy enhanced, protecting individual autonomy and giving people control over their personal data. And it should be fair, with harmful bias managed, meaning the system is evaluated for systemic, statistical, and human bias that could produce discriminatory outcomes.
These characteristics give a compliance team a concrete checklist when a vendor claims its AI is trustworthy without defining the term.
NIST AI RMF vs ISO/IEC 42001 vs the EU AI Act
The AI RMF is not the only framework a compliance team will run into. Here is how it compares to the two most common alternatives.
| FRAMEWORK | TYPE | SCOPE |
|---|---|---|
| NIST AI RMF | Voluntary framework | Risk management guidance across the AI lifecycle, for any organization |
| ISO/IEC 42001 | Certifiable management system standard | A formal AI management system that can be audited and certified by a third party |
| EU AI ACT | Binding law | Risk tiered legal obligations for AI systems placed on the EU market |
ISO/IEC 42001, published in December 2023, is the AI equivalent of ISO 27001: a certifiable management system standard an organization can be formally audited against by a third party. The EU AI Act, which entered into force in August 2024, is different in kind. It is binding law with risk tiered obligations, and under amendments that took effect in 2026, high risk systems in sensitive areas such as biometrics and critical infrastructure now face a compliance deadline of December 2027, with high risk systems embedded in regulated products following in August 2028. Many U.S. companies adopt the NIST AI RMF first because it is free, flexible, and maps cleanly onto both of the others, then layer ISO 42001 certification or EU AI Act compliance on top as their AI footprint and client base require it.
How Regulated Teams Use the NIST AI RMF to Evaluate AI Vendors
Most compliance teams do not build their own AI models. They evaluate someone else's, whether that is an AI feature inside a SaaS tool, a chatbot vendor, or the AI capability inside a proposal or response management platform. The AI RMF's Map function is built for exactly this kind of evaluation.
A practical vendor review walks through a short set of questions drawn from the framework. Where does the vendor's model run, and does customer data leave the organization's environment? Is the model trained on customer prompts, or is it isolated to a private instance? What happens when the AI generates an answer that is wrong, and who reviews it before it reaches a client? Is there an audit trail showing who approved each AI generated output?
These are close to the same questions that show up in SIG, CAIQ, and custom AI specific sections of security questionnaires, which makes the AI RMF a useful internal checklist before a team ever sends the questionnaire back. RocketDocs built its own AI engine, Astro, around this model: it runs inside a private environment, drafts only from a customer's approved content library, and logs every generated answer for review, the pattern the Govern and Manage functions call for. Teams evaluating their own AI vendor risk can see how that architecture holds up against the AI RMF in RocketDocs' private AI overview.
Getting Started: A Simple NIST AI RMF Checklist
Teams do not need to implement all four functions at once. A reasonable starting sequence begins with an inventory of every AI system and AI vendor currently in use, including AI features quietly turned on inside existing software. Next, assign an owner for AI governance decisions, even if that is a committee rather than one person. Map the data each AI system touches and where it is processed. Test the highest risk systems first against the seven trustworthy AI characteristics. Finally, document the review in a format an auditor or client can read on request.
Teams already handling security questionnaires can fold this work into their existing security questionnaire response process rather than standing up a separate program from scratch.
Looking for the platform behind this? See the RocketDocs platform or book a demo.


