
Vendor due diligence is the review a buyer runs on a supplier before and during a contract, covering security, financial stability, legal standing, operations, and compliance. The buyer sends questionnaires and requests evidence; the vendor supplies answers and documents. In regulated industries it repeats on a set cycle rather than happening once.
What vendor due diligence covers
Due diligence is rarely one questionnaire. It is a set of parallel reviews run by different teams inside the buying organization, each testing a different kind of risk and each with its own idea of what sufficient evidence looks like. The table below maps the domains that come up most often.
| DOMAIN | WHAT THE BUYER IS TESTING | WHAT THEY TYPICALLY REQUEST |
|---|---|---|
| Security | Whether your controls protect their data | SIG or CAIQ workbook, SOC 2 report, penetration test summary |
| Financial | Whether you will still be operating in three years | Audited statements, credit check, funding history |
| Legal and contractual | Liability, IP ownership, and corporate standing | Contracts, litigation history, corporate registration |
| Operational | Whether you can deliver at the agreed service level | Business continuity plan, support model, staffing detail |
| Privacy and data | Where data lives and who else can touch it | Subprocessor list, data flow diagram, transfer mechanisms |
| Compliance | Whether you meet the rules that bind the buyer | Certifications, attestations, policy documents |
The practical consequence for the vendor is that one due diligence request often arrives as four or five separate asks, on different timelines, from people who do not talk to each other. Security sends a spreadsheet. Procurement sends a supplier form. Legal sends a redline. Finance asks for statements. Answering each one from scratch is how a two week request becomes a two month one.
Who runs vendor due diligence, and when
On the buyer side, vendor due diligence usually sits with procurement or a third-party risk function, with security, legal, finance, and compliance acting as reviewers. In banking and financial services the expectations are written down. The Interagency Guidance on Third-Party Relationships: Risk Management, issued in June 2023 by the Federal Reserve, the FDIC, and the OCC, organizes third-party risk into a life cycle: planning, due diligence and third-party selection, contract negotiation, ongoing monitoring, and termination. Due diligence is a named stage in that life cycle, and ongoing monitoring means the review does not end at signature.
Onboarding versus recurring review
First-time diligence is the heaviest. It establishes a baseline: who you are, how you operate, what data you hold, and what happens if you fail. Recurring review is narrower but more frequent, often annual, and it asks a different question, which is what changed. New subprocessors, a new hosting region, a lapsed certificate, a material incident, a change of control. Vendors who treat the annual refresh as a brand new questionnaire spend far more time on it than the request actually requires.
The evidence buyers request
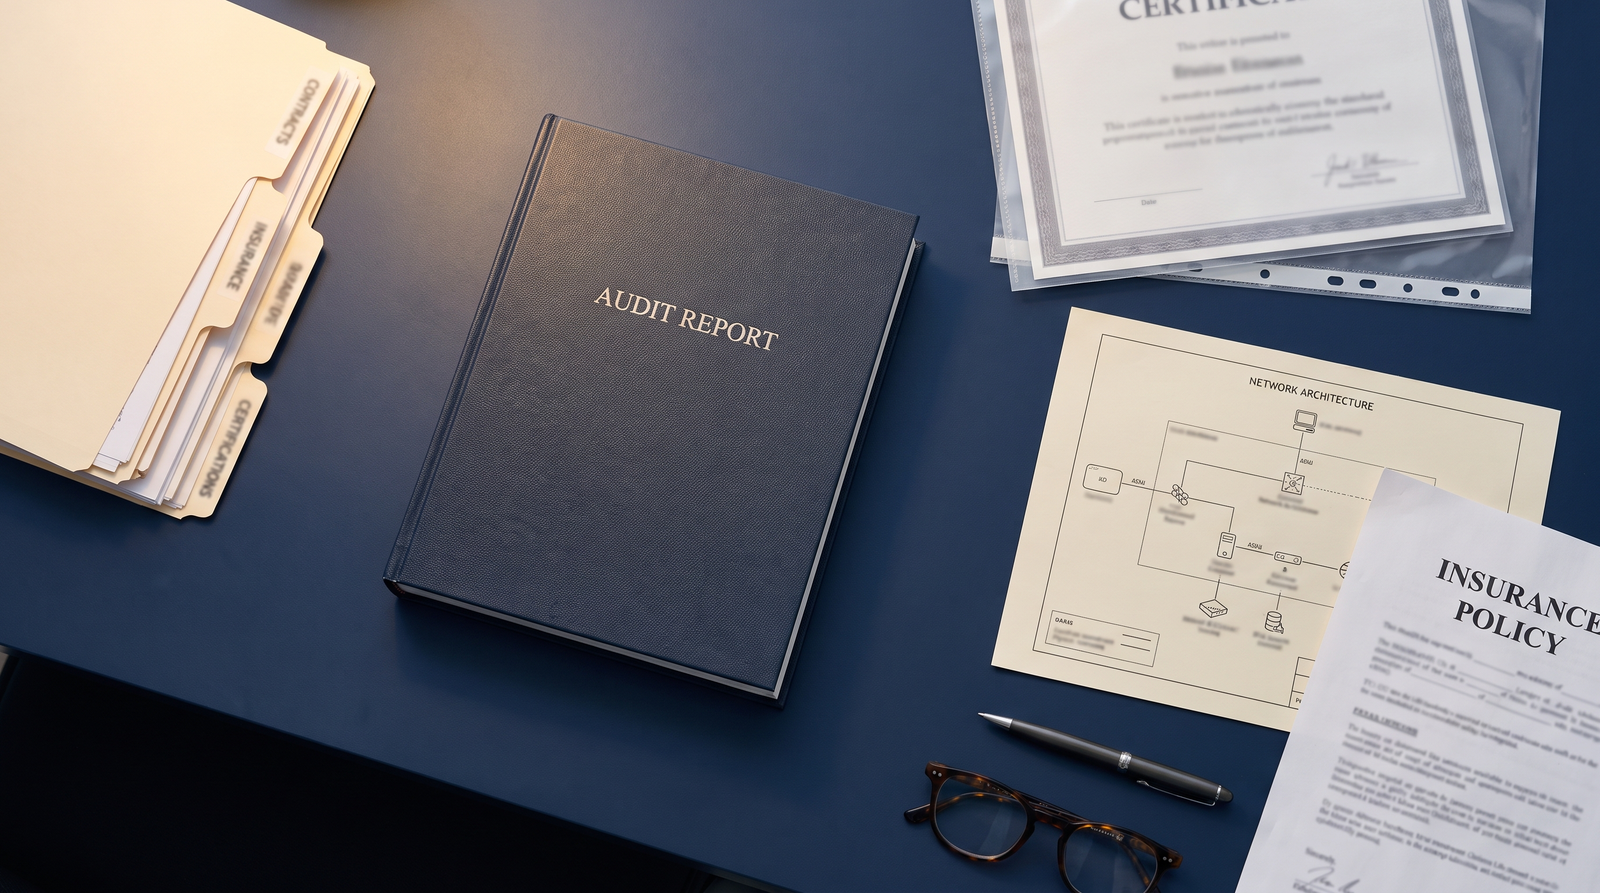
Most of the document set is predictable, which is what makes it worth assembling in advance rather than under deadline. Common requests include a current SOC 2 Type II report or ISO 27001 certificate, a penetration test summary, proof of cyber liability insurance, a business continuity and disaster recovery plan, a subprocessor list, an architecture or data flow diagram, security policies, financial statements, and tax documentation.
Security diligence increasingly leans on standardized questionnaires rather than bespoke ones, which works in the vendor's favor. If you already maintain a completed SIG or CAIQ workbook, much of what the next buyer asks for is a mapping exercise rather than new writing, a pattern covered in more depth on our security questionnaires page. Supply chain diligence often borrows its structure from NIST SP 800-161 Rev. 1, updated in November 2024, which sets out cybersecurity supply chain risk management practices for systems and organizations.
Why vendor due diligence stalls on the vendor side
The delay is rarely that the answer does not exist. It is that the answer exists in four places, in three versions, and nobody is certain which one is current. A security engineer answered the encryption question for one buyer in March. Someone in legal answered it differently in May. Sales has a third version in a deck. When the next questionnaire lands, someone has to adjudicate, and the adjudication is the bottleneck, not the typing.
The second cause is expert dependency. A small number of people hold the answers to the hardest questions, and those people have day jobs. Every request routed to them competes with their actual work, so turnaround becomes a function of their calendar rather than the deadline printed on the questionnaire.
How to respond to vendor due diligence faster
Maintain one approved answer library
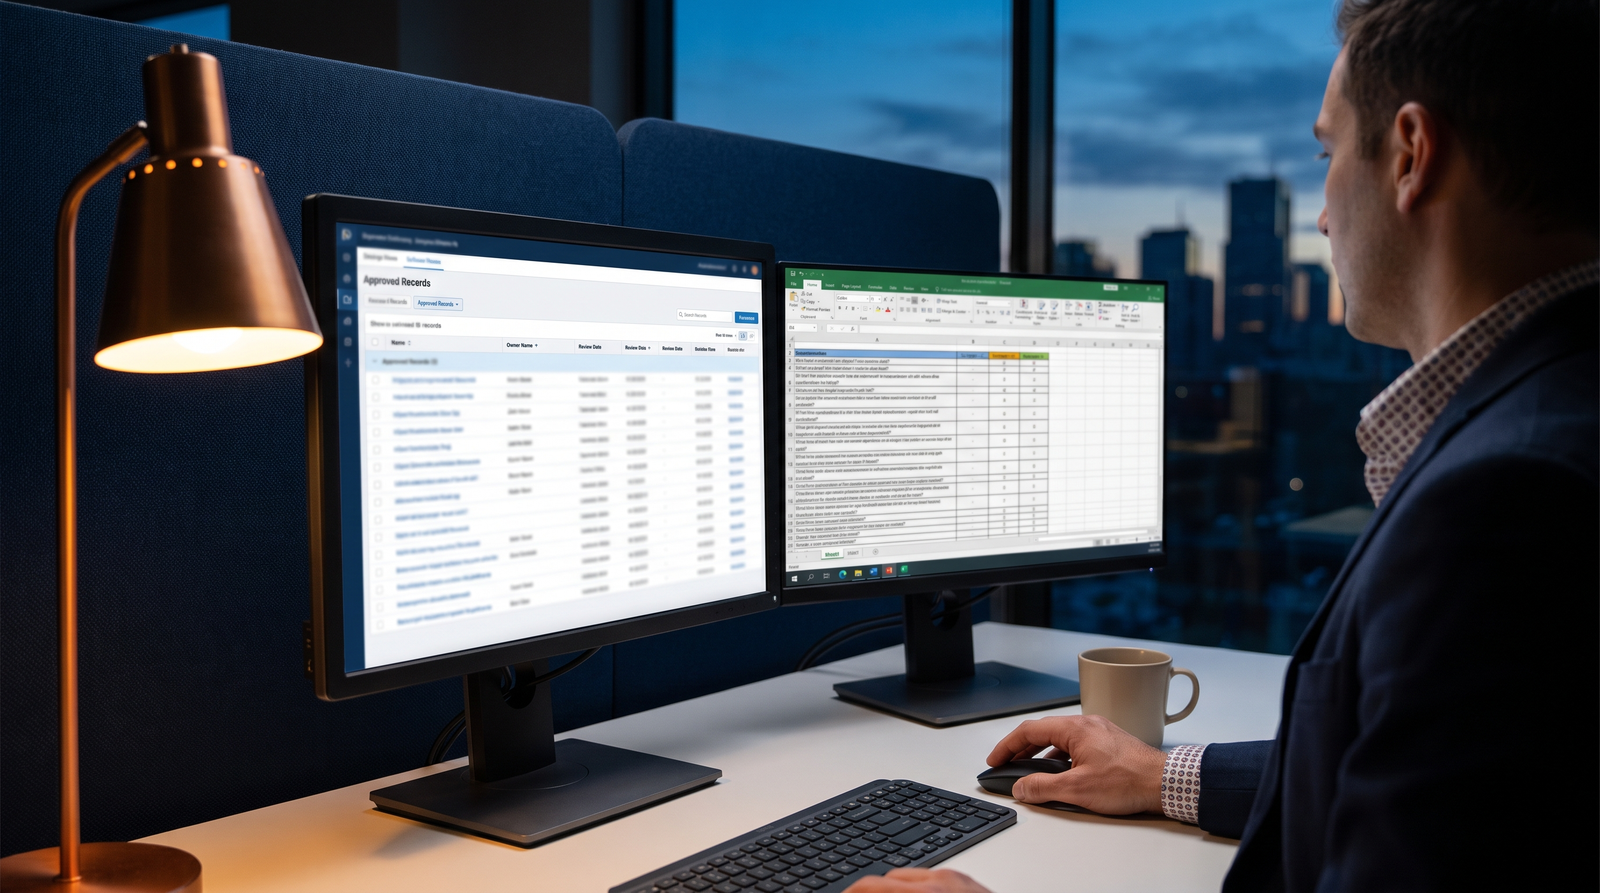
The highest leverage change is moving from answer on demand to answer once and reuse. Treat the approved answer set as institutional knowledge rather than proposal scrap: one record per question, one owner, one review date, and a status that tells a responder whether it can be used as written. That is the core idea behind Knowledge-Centered Success, the methodology maintained by the Consortium for Service Innovation, which holds that knowledge should be captured in the workflow that uses it and improved as it is reused rather than written up separately afterward. The Consortium publishes the KCS principles and practices openly, and they translate directly to questionnaire response work.
Give every answer an owner and a review date
Answer libraries decay quietly. The fix is metadata rather than discipline. Name an owner for each answer and set a review date, then route the review to the owner when it comes due instead of when a questionnaire lands. That turns expert involvement into a scheduled, predictable load rather than an emergency, which is the difference between a two day turnaround and a three week one. A content library built for this keeps ownership and review history attached to the answer itself.
Keep the evidence pack current and versioned
Documents expire on their own schedule. A SOC 2 report covers a defined period. Certificates lapse. Insurance renews. Keep one current version of each artifact with its expiry recorded, so whoever answers a diligence request is never guessing which file to attach. Recurring investor and regulatory reviews work the same way, which is why teams handling DDQ completion at volume tend to solve the evidence problem and the answer problem together.
Vendor due diligence is not going to get lighter. Buyers in regulated industries are under explicit supervisory expectations to review their suppliers and to keep reviewing them, and the questionnaires reflect that. The vendors who handle it well are not the ones with the best answers. They are the ones who can find their best answer, confirm it is still true, and send it before the deadline.
Looking for the platform behind this? See the RocketDocs platform or book a demo.


